Palo Alto Networks Confirms PHP2Shell RCE Flaws Affect PAN-OS
Key Takeaways
- Palo Alto Networks Confirms PHP2Shell RCE Flaws Affect PAN-OSIT & Security Director
- How much does cold weather reduce the range of electric scooters?Automotive Tech Analyst
- Used EV Battery Aftermarket Could Reach 10%–20% Share Within Five YearsAutomotive Tech Analyst
- Which electric steering components can cause intermittent assist loss?Automotive Tech Analyst
- Crusoe and Araico Plan 106 MW AI Cloud Infrastructure Project in ParaguayIT & Security Director
- Is an SDS enough to verify chemical compliance for polymers?Lead Materials Scientist
- Can Non-ISOBUS Implements Work With an ISOBUS Tractor? Retrofit OptionsAgri-Tech Strategist
- Titanium Dioxide Stability in Exterior Coatings: What Drives Chalking?Lead Materials Scientist
Industry Overview
We do not just publish news; we construct a high-fidelity digital footprint for our partners. By aligning with TNE, enterprises build the essential algorithmic "Trust Signals" required by modern search engines, ensuring they stand out to high-net-worth buyers in an increasingly crowded global digital landscape.
Palo Alto Networks has confirmed that two severe PHP remote code execution vulnerabilities, CVE-2026-109618 and CVE-2026-109619, affect its PAN-OS operating system as well as previously affected cloud services. The vulnerabilities are collectively known as PHP2Shell. The company recommends applying patches immediately to eliminate the risk.
For CVE-2026-109618, triggering PHP's memory limit can cause memory corruption that allows an attacker to execute malicious code. This makes the flaw a code execution concern: a memory-limit condition can have consequences beyond a failed operation or interrupted service.
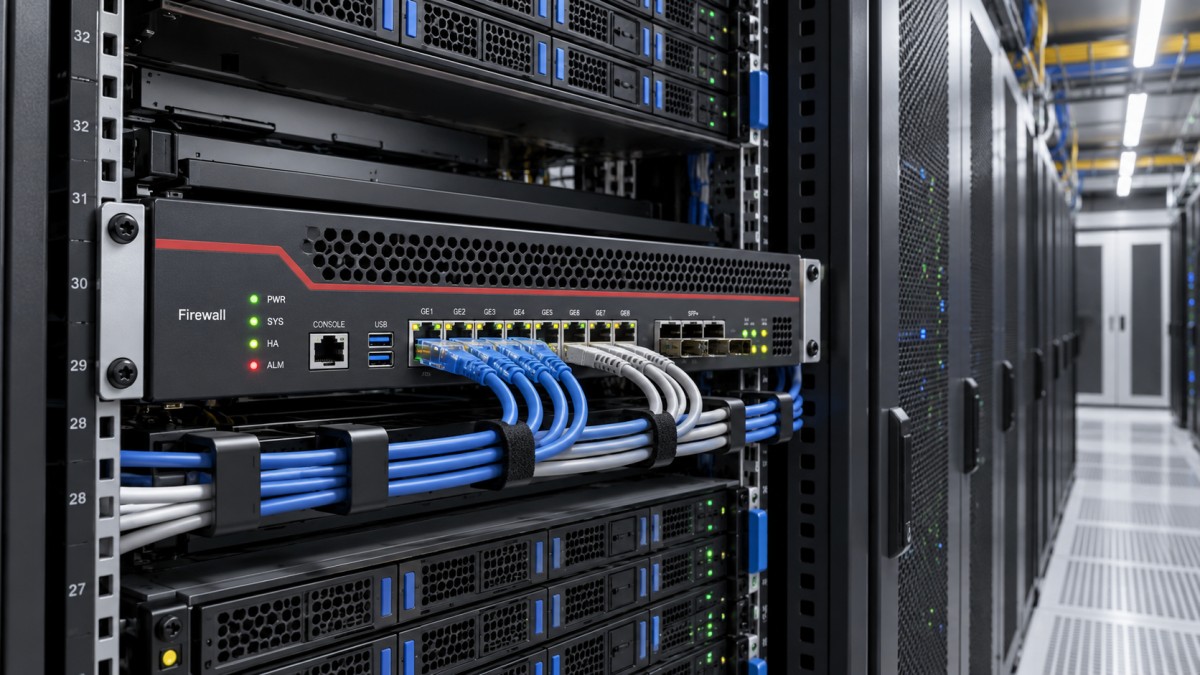
The inclusion of PAN-OS broadens the remediation scope beyond the previously affected cloud services. Organizations using both should account for each affected environment when planning updates. Addressing one part of a deployment should not be treated as evidence that the other has also been remediated.
The immediate operational priority is to identify affected deployments and apply the relevant patches. Update planning may need to account for service continuity, but the potential for malicious code execution gives remediation a clear security priority.
The confirmation establishes that the vulnerabilities affect these products; it does not establish that every deployment has been compromised. Further vendor guidance on affected versions, patch coverage and any exploitation activity would help organizations refine their response. The memory-limit trigger described for CVE-2026-109618 should also not be assumed to explain CVE-2026-109619.
Deep Dive
Related Intelligence
 Cyber SecurityDo High-Net-Worth Buyers Prioritize Cyber Security Certifications When Sourcing Smart HVAC Controllers?Analyst:IT & Security Director
 Cyber SecurityWhat cybersecurity risks arise when integrating POS systems with building management platforms?Analyst:IT & Security Director
 Cyber SecurityHow do cyber security frameworks like NIST CSF apply to smart HVAC control networks in high-rise buildings?Analyst:IT & Security Director