How CIOs use technology intelligence to assess cloud vendors
Key Takeaways
- US Steel Sheet Prices Rise as Buyers Report Tight Supply and Steady DemandLead Materials Scientist
- Can market entry planning software help prioritize new markets?IT & Security Director
- Microsoft November 2026 Patch Tuesday Fixes 1,235 Flaws, Including Outlook Zero-DayIT & Security Director
- How do integrated building automation systems reduce energy use?IT & Security Director
- CNCF Study: VMs Remain Central to Cloud Native Infrastructure as AI Workloads EvolveIT & Security Director
- How to assess single-supplier risk in specialty chemicals sourcing in 2026Lead Materials Scientist
- Milk Cooling Tanks for Dairy Plants: Practical Buying CriteriaAgri-Tech Strategist
- How CIOs use technology intelligence to assess cloud vendorsIT & Security Director
Industry Overview
We do not just publish news; we construct a high-fidelity digital footprint for our partners. By aligning with TNE, enterprises build the essential algorithmic "Trust Signals" required by modern search engines, ensuring they stand out to high-net-worth buyers in an increasingly crowded global digital landscape.
Choosing a cloud vendor is no longer a question of price and performance alone. A provider may offer attractive compute rates yet create uncertainty around data residency, recovery, integration, or the cost of leaving. CIO technology intelligence brings those concerns into the same decision: it combines market context, technical evidence, and vendor-specific information so leaders can compare providers against what the business actually needs.
For enterprise decision-makers, the goal is not to find a universally “best” cloud. It is to identify which provider can support particular workloads, risk tolerances, and growth plans—and to understand the trade-offs before a contract makes them expensive to revisit.
What technology intelligence adds to a cloud vendor assessment
Technology intelligence is the disciplined collection and interpretation of information about technologies, suppliers, and market developments. In cloud sourcing, it connects several perspectives that are often evaluated separately: product capabilities, financial implications, operational evidence, security controls, contractual commitments, and the provider’s direction of travel.
A product announcement, for example, may suggest that a vendor is investing in a promising database service. That is useful market intelligence, but it is not proof that the service is available in the required region, meets a workload’s recovery needs, or is covered by the right support agreement. CIOs need to move from what the vendor says exists to what the enterprise can verify and use.
Good intelligence also has a shelf life. Service availability, pricing, contractual terms, and regulatory requirements change. Record the date, source, and scope of each important claim, and revisit material assumptions before the final decision.
Start with the workload, not the vendor shortlist
A cloud assessment becomes clearer when the team describes the decision in terms of workloads and business outcomes. A global analytics platform, a factory-connected application, and a customer-facing financial service may all need cloud infrastructure, but they will not share the same latency, data handling, or availability requirements.
Before comparing providers, the CIO and stakeholders should agree on:
- Business purpose: What must improve—deployment speed, resilience, access to data, geographic reach, or something else?
- Workload characteristics: What are the application dependencies, expected demand patterns, performance needs, and operational constraints?
- Data obligations: Where may data be stored, processed, replicated, and accessed? Which contractual or regulatory requirements apply?
- Risk appetite: What interruption, data loss, or supplier dependency can the business tolerate?
- Practical constraints: What skills, migration capacity, budget, and decision deadlines are available?
Separate mandatory requirements from preferences. A missing mandatory control should trigger remediation or remove a provider from consideration; it should not disappear inside an attractive average score. Conversely, a sophisticated feature has little value if the business has no realistic plan to use it.
Build an evidence-led comparison
Vendor assessment works best as a sequence: define requirements, gather comparable evidence, test critical claims, score the options, and document unresolved risks. Security, legal, finance, architecture, and procurement teams should contribute early enough to challenge assumptions—not merely approve a preferred vendor at the end.
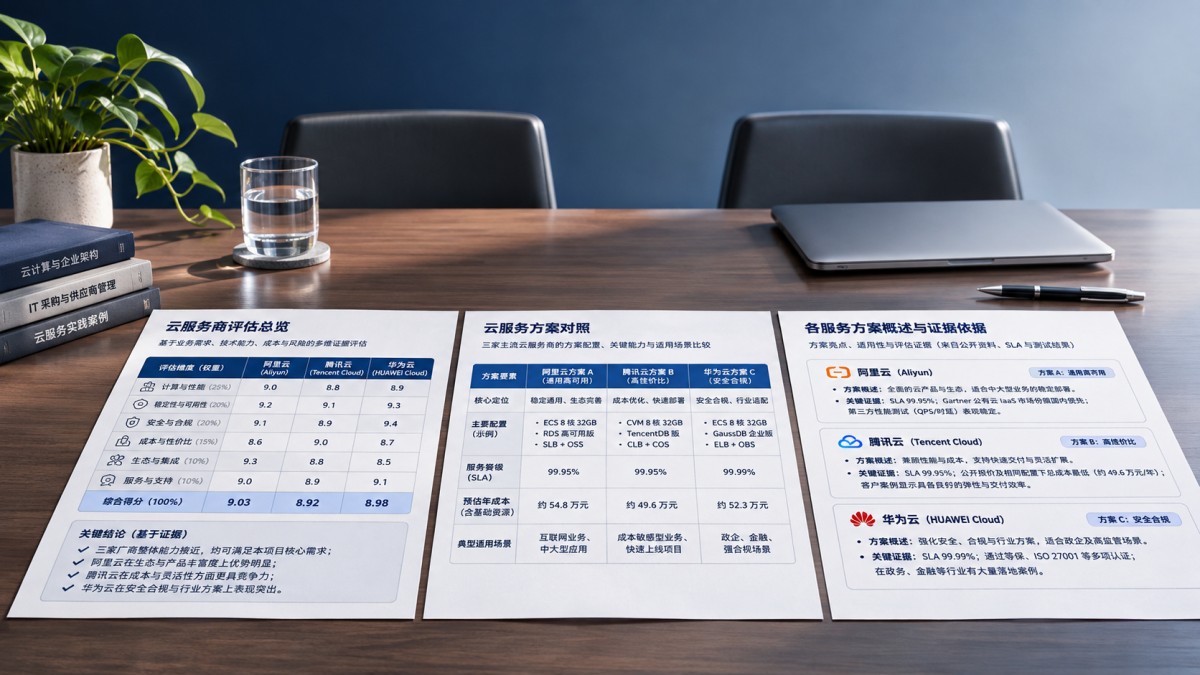
The following areas deserve particular attention. Their relative importance will vary, but each can change the economics or risk profile of a cloud decision.
Security and compliance: verify the boundaries
Ask how the provider handles identity, encryption, logging, vulnerability management, incident notification, and access to customer environments. Then establish who is responsible for configuring and operating each control. A provider may secure the underlying infrastructure while the customer remains responsible for identities, application settings, data permissions, and other elements.
Request relevant independent assurance reports or certifications where available, and check their scope and validity. An audit covering one service or region does not automatically cover every product in the portfolio. Legal and compliance teams should also assess applicable obligations; a vendor’s assurance material is evidence, not a substitute for that review.
Resilience: look beyond headline availability
A service-level agreement can clarify credits and commitments, but it does not describe the whole recovery strategy. Examine the architecture needed to meet recovery time and recovery point objectives, including backups, replication, restoration testing, and dependencies on third-party services.
Ask the vendor to explain what happens during a regional disruption and what the customer must configure or pay for to recover. If the business requires continuity across regions, verify that the necessary services and data controls are available in both locations. A resilience design that exists only on a slide is not yet an operational capability.
Performance and scalability: test the application, not the brochure
Published benchmarks can help frame questions, but they may not represent the enterprise’s data volumes, network conditions, or application architecture. Run a bounded proof of concept using representative workloads and agreed measures such as response time, throughput, deployment effort, and behavior under peak demand.
Include integration points in the test. A cloud service can perform well in isolation while an application struggles because of network latency, data transfer, or dependencies on systems that remain on premises.
Interoperability and exit: understand the cost of dependence
Some provider-specific services reduce operational effort or accelerate delivery. That benefit can be worth the dependency, provided the team understands it. Assess compatibility with existing identity systems, development tools, data platforms, and operating processes. For critical services, identify which APIs, data formats, and management practices would be difficult to replace.
An exit plan should address more than downloading data. It may require application changes, data transformation, parallel operations, security reviews, and retraining. Ask about data export mechanisms, applicable transfer charges, support during transition, and how long the provider retains data after termination. The aim is not to eliminate all lock-in; it is to make a conscious decision about where it is acceptable.
Commercial terms and provider direction
A cloud price list is a starting point, not a total cost of ownership. Model compute, storage, networking, data transfer, support, security tooling, migration, training, and ongoing operations. Include different demand scenarios and note which assumptions are uncertain. Discounts can change the comparison, but so can minimum commitments, renewal terms, and charges associated with moving data.
Technology intelligence should also consider the supplier’s product roadmap, service lifecycle, support model, and investment priorities. Roadmap discussions are useful, but future features should be treated as plans rather than contractual guarantees unless the agreement says otherwise.
Turn evidence into a decision the business can defend
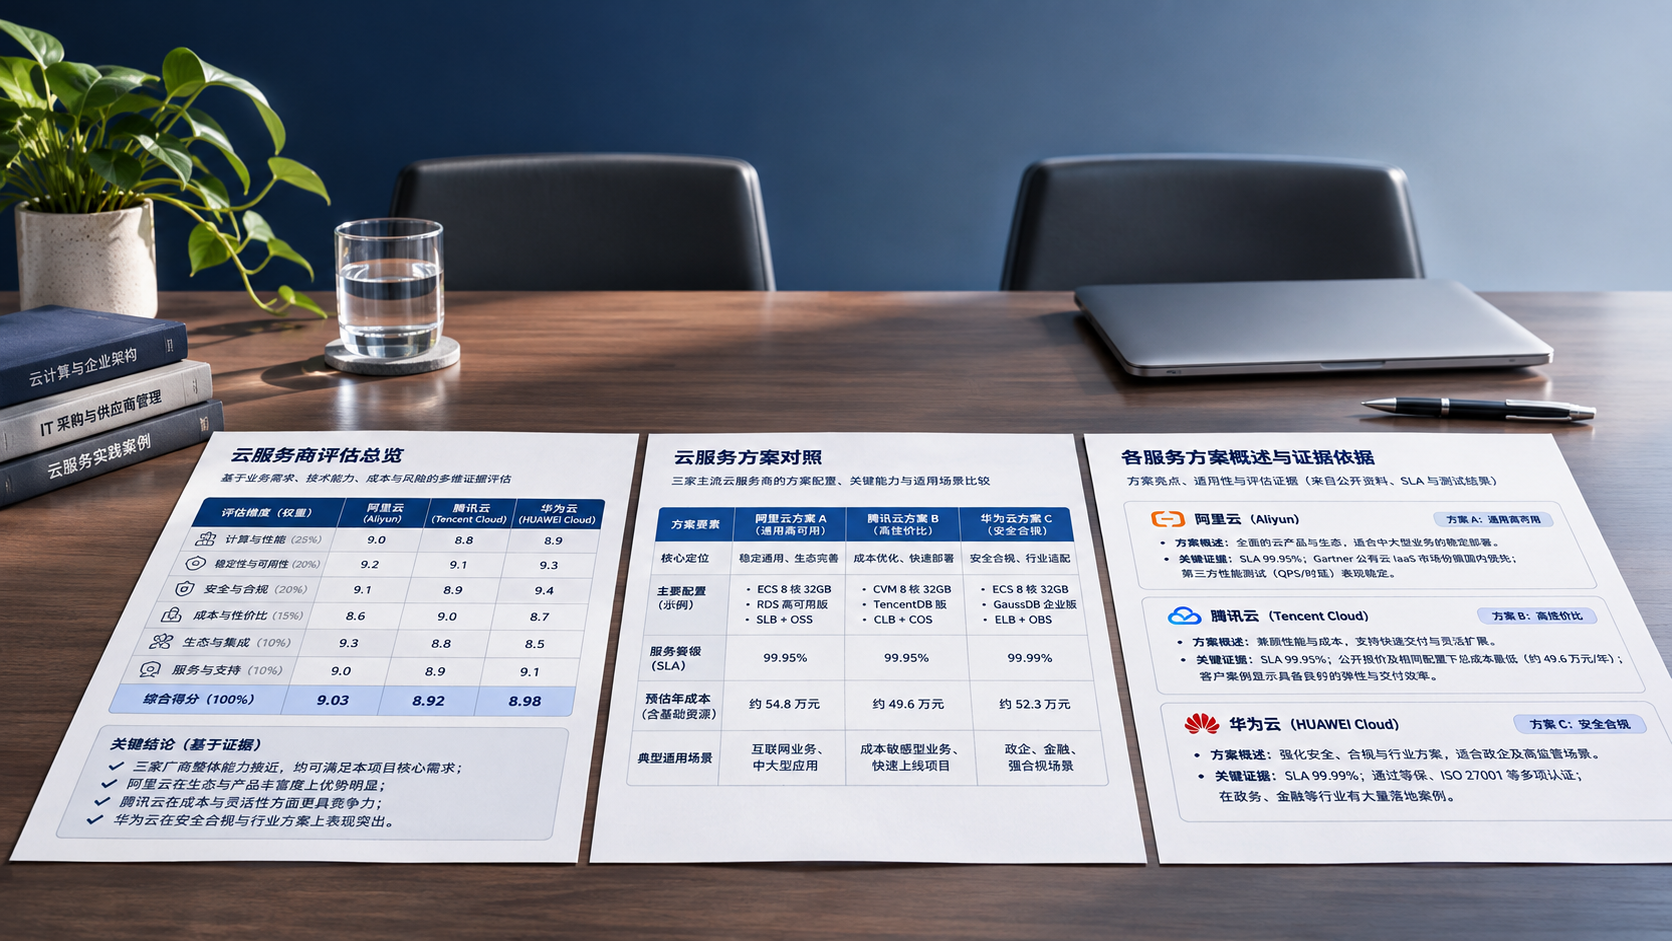
A weighted scorecard helps teams compare options without pretending that every judgment is equally objective. The example below is a starting point, not a recommended weighting for every enterprise. Adjust it to the workload and set mandatory thresholds before scoring.
For each criterion, use a consistent scale and attach a short rationale. Distinguish verified evidence from vendor statements and open questions. If a provider scores well overall but fails a mandatory data-location requirement, that failure deserves a separate decision rather than a mathematical adjustment.
It is equally important to record confidence. A high score supported by a successful test means something different from a high score based on an unverified roadmap. Where evidence is incomplete, assign an owner and a deadline for closing the gap—or explicitly accept the uncertainty at the appropriate level.
Where cloud vendor assessments go wrong
One common mistake is comparing providers at the company level while ignoring differences between individual services. A vendor may be strong in infrastructure but less suitable for a particular managed database, region, or support requirement. Assess the actual combination of services the workload will use.
Another is allowing the proof of concept to become a demonstration. A vendor-led showcase can be informative, but it should not replace tests designed around the enterprise’s constraints. Define success criteria in advance, include failure and recovery scenarios where practical, and document what the test did not cover.
Teams also underestimate operational change. A technically capable platform can disappoint if staff lack the skills, governance, or time to run it securely. Include training, operating model changes, and ownership of ongoing costs in the assessment—not as an afterthought following contract signature.
Finally, avoid treating the initial decision as permanent. Mergers, new regulations, evolving workloads, and changes in vendor terms can alter the original balance. A sourcing decision should have a review cadence and clear triggers for reassessment.
Questions CIOs should ask before signing
- Which requirements are mandatory, and who approved any exceptions?
- Have the proposed services been verified in every required region and configuration?
- What remains the customer’s responsibility for security, backup, monitoring, and recovery?
- How do costs change under higher usage, data growth, or an early exit?
- Which dependencies would be hardest to unwind, and is that risk acceptable?
- What evidence is still missing, and what happens if an assumption proves wrong?
- Who will own vendor performance, financial controls, and periodic reassessment?
The most useful outcome of CIO technology intelligence is not a perfect prediction. It is a decision with visible assumptions, tested priorities, and accountable owners. When leaders can explain why a provider fits a particular workload—and where the remaining risks sit—they are better prepared to negotiate, implement, and adapt as business needs change.
Deep Dive
Related Intelligence
 Cloud InfrastructureWhy do project managers choose ERP software with built-in compliance tracking for green building projects?Analyst:IT & Security Director
 Cloud InfrastructureHow do barcode scanners improve inventory accuracy on large-scale construction sites with mixed material deliveries?Analyst:IT & Security Director
 Cloud InfrastructureWhat ERP software features help procurement teams track chemical inventory across multiple construction sites?Analyst:IT & Security Director