National Cybersecurity Standards Committee Seeks Feedback on Three Guidelines
Key Takeaways
- How to verify supplier credentials in global chemical sourcingLead Materials Scientist
- National Cybersecurity Standards Committee Seeks Feedback on Three GuidelinesIT & Security Director
- How to verify specialty chemical exporters in IndiaLead Materials Scientist
- Trump Fires National Cyber Director, Names Kirsten Davies Acting DirectorIT & Security Director
- Can mobile POS systems accept payments without internet access?IT & Security Director
- Malaysia and US Deepen Sovereign AI Cloud Cooperation, With $50 Million in US SupportIT & Security Director
- How chemical recycling is reshaping plastics technology in EuropeLead Materials Scientist
- CISA Warns Organizations to Patch Oracle Java Java4Shell VulnerabilityIT & Security Director
Industry Overview
We do not just publish news; we construct a high-fidelity digital footprint for our partners. By aligning with TNE, enterprises build the essential algorithmic "Trust Signals" required by modern search engines, ensuring they stand out to high-net-worth buyers in an increasingly crowded global digital landscape.
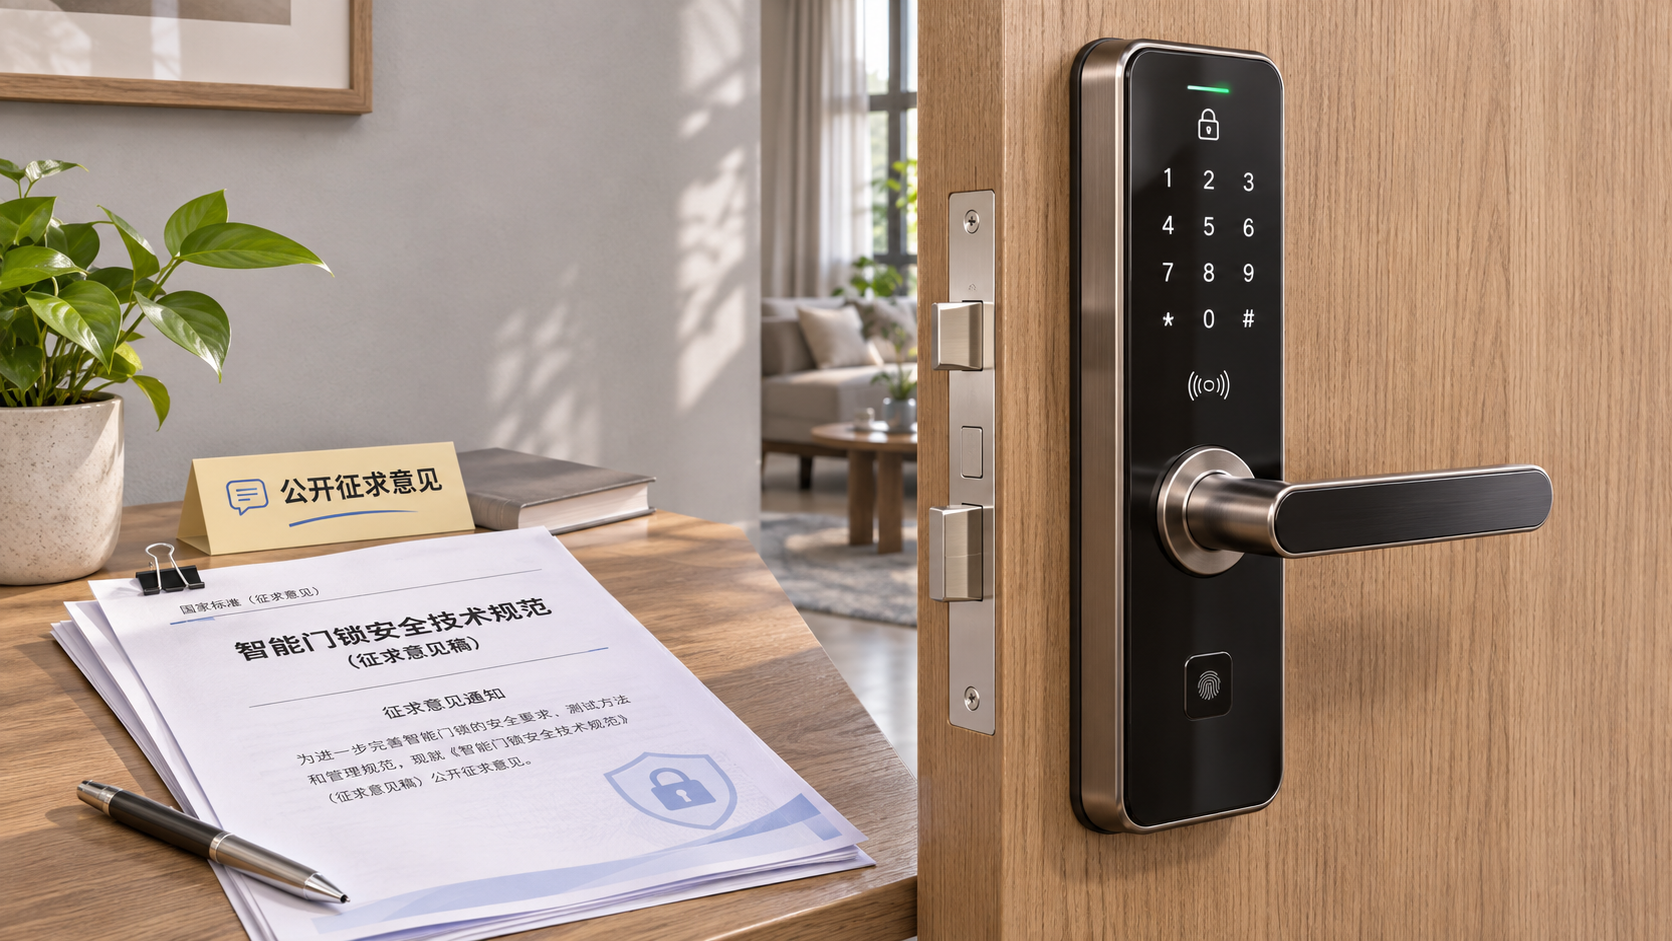
The secretariat of the National Cybersecurity Standardization Technical Committee has opened a public consultation on three cybersecurity standards practice guidelines, including security requirements for consumer smart door locks carrying a cybersecurity label. The event date was not specified in the information provided. For manufacturers, suppliers, buyers and organizations involved in product assessment, the consultation is worth watching because its eventual outcome could influence how security expectations are documented and assessed across connected product supply chains.
Three Practice Guidelines Open for Comment
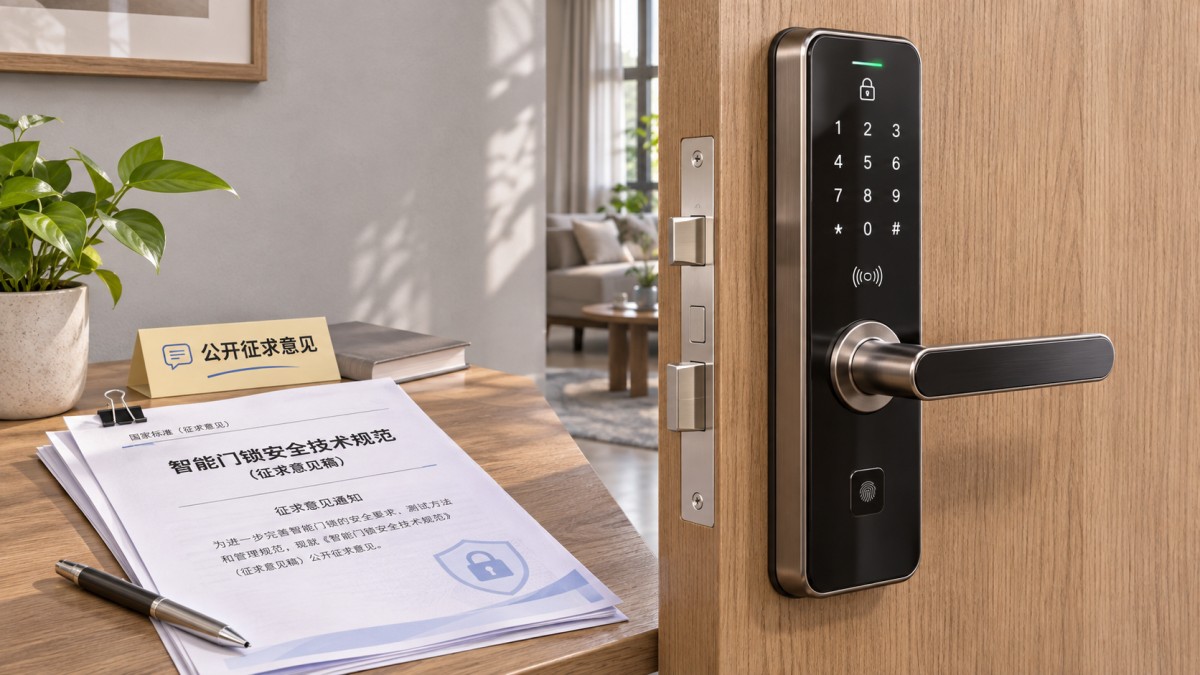
The committee secretariat issued a notice seeking public comments on three cybersecurity standards practice guidelines. One addresses security requirements for consumer smart door locks associated with a cybersecurity label. The stated purpose is to clarify security requirements for consumer smart door locks and related products covered by cybersecurity labels and to improve the security protection of internet-connected terminal devices.
The information provided does not identify the other two guidelines, specify when the notice was issued or describe the consultation timetable. It also does not state the technical requirements, assessment procedures or implementation arrangements for the guidelines.
Where Proposed Security Requirements Could Reach the Supply Chain
Product teams and component suppliers
From an industry perspective, smart lock manufacturers may be the most directly interested participants because the named guideline concerns the security of their products. If the consultation leads to a finalized document with detailed requirements, manufacturers may need to compare those requirements with product designs, supporting documentation and the information they receive from component or software suppliers. The input does not establish what that comparison would involve, so any assessment remains preliminary.
Suppliers may also need to respond to more detailed questions from manufacturers if buyers begin asking how product security is supported. Depending on the eventual text and commercial arrangements, those questions could concern how a component fits into a connected lock or what evidence is available to support a product assessment. The consultation itself does not establish a new obligation for every supplier, and the scope of any eventual requirement remains to be verified.
Buyers and distribution channels
For purchasers and distributors, the practical issue may be whether future product specifications or sales documentation refer to the finalized guidelines or associated cybersecurity labels. A buyer comparing smart locks could eventually ask suppliers to explain a product's security claims or provide supporting material. That is a possible procurement response, not a confirmed change to purchasing rules.
Analysis also suggests that the distinction between a proposed guideline, a label and a contractual requirement could matter during supplier selection. A product claim should be understood in the context in which it is made: the available information does not establish that the consultation has created a mandatory label, a purchasing condition or a prohibition on products without one. Buyers can avoid premature conclusions by checking any future tender language against the final official text and the terms of the purchase.
Assessment services and delivery partners
Testing, certification and other product assessment providers may wish to follow the consultation because a finalized guideline could affect the questions clients ask about demonstrating security. However, the input does not confirm that a new certification scheme, testing method or accredited assessment process has been established. Any future service scope would depend on the documents and implementation arrangements ultimately issued.
Installers, integrators and after-sales providers could also face requests for clearer product information if purchasers connect security expectations with delivery and support. Whether those requests arise, and what they cover, would depend on the final guidance and individual contracts. At present, the notice is a reason to review information flows among parties, rather than evidence that delivery or service procedures have already changed.
Trade and supplier documentation
Businesses that source or sell connected locks across supply chains may need to monitor whether future buyers incorporate the eventual guidance into specifications. This could affect the timing of document collection or product review in particular transactions. The information provided does not identify a change to customs procedures, export conditions or market access, so no such change can be inferred from the consultation.
For commercial teams, a useful distinction is between a formal requirement that may appear in an eventual official document and a security condition negotiated by a customer. Either could matter to a transaction, but their scope and consequences would need to be checked separately. A request in a future contract should not automatically be treated as proof of a general regulatory obligation.
Preparing for the Next Version of the Guidance
Identify products and claims that may need review
Manufacturers and suppliers could begin by identifying the consumer smart locks and related labelled products in their portfolios, along with the security claims and supporting materials already used for them. This is a preparation step, not a requirement established by the input. It can make a later comparison more manageable if the final guidance defines relevant product categories or evidence expectations.
Teams should avoid assuming that all connected devices will fall within the same scope. The summary refers to consumer smart door locks and related products associated with cybersecurity labels, but it does not describe the boundaries of the three documents. The titles and full text of all three guidelines would therefore be important before assigning responsibilities or estimating the extent of any product review.
Check the official text and any assessment arrangements
When the relevant documents are available, companies can examine the proposed language, any revisions following consultation and subsequent official explanations. Particular points to verify include which products are covered, how security requirements are expressed and whether any label or assessment process is described. These are questions for verification; the input does not provide their answers.
It would also be prudent to distinguish a practice guideline from any separate contractual, certification or regulatory instrument that may later refer to it. The notice confirms a consultation, but the information provided does not establish the legal status of the final documents or how any assessment might be conducted. Those points should be checked against authoritative material before being reflected in compliance commitments.
Review evidence before making commitments
Product, procurement and commercial teams could map the documentation they already hold against the information customers may reasonably request. Depending on the final text and the transaction, relevant materials might include product specifications, technical documentation or existing test reports. Their existence would not by itself demonstrate conformity with an unidentified requirement, and the input does not say that any particular document is mandatory.
Where evidence depends on a supplier, early discussion may help establish who can provide it and how it can be kept current. Buyers could similarly ask prospective suppliers to identify the basis of security or label claims without presuming that a new assessment process is already in operation. Such checks can support more precise contract discussions while leaving room for the official position to develop.
Keep procurement and delivery plans adaptable
If a future customer specification refers to the final guidelines, additional review or documentation could affect an individual order's preparation time. That possibility is not evidence of an industry-wide delay. Companies planning purchases or deliveries can monitor customer communications and consider how they would handle a request for additional evidence, including whether an alternative product would need separate verification.
After-sales teams may also benefit from knowing which product documents and supplier contacts are available when a customer raises a security question. The consultation does not establish new support duties, but consistent records could make it easier to answer transaction-specific questions if expectations change. Decisions about timing and resources should remain proportionate to the information actually released.
A Consultation Signal, With Implementation Still to Be Clarified
In this publication's assessment, the notice is best understood as a developing standards signal. It shows that security requirements for labelled consumer smart locks and related products are being considered through a public consultation. The available information does not establish that the proposed text is final or that a new set of requirements is already being enforced.
What happens next will matter more to business decisions than the consultation headline alone. The content of the other two guidelines, the detailed scope of each document, any changes made after comments and any official explanation of implementation could all affect how companies interpret the initiative. Feedback from manufacturers, buyers and assessment providers may also help clarify which parts of a proposal require further definition, although the input does not report any such feedback.
Market practice may develop at a different pace from the documents themselves. Some customers could choose to ask questions while the consultation remains open, while others may wait for a finalized text. Neither response should be presented as an established market trend on the basis of the information available here. The immediate task is to distinguish confirmed documents and customer instructions from expectations that are still being discussed.
What Businesses Can Take from the Notice Today
The consultation places consumer smart lock security and cybersecurity labels on the agenda for standards development. Its potential relevance extends from product design and supplier evidence to purchasing and delivery discussions, but the size and nature of any effect remain uncertain. A proportionate response is to identify potentially relevant products, follow official updates and prepare to assess the final wording before treating any proposed provision as an operative requirement.
Basis for This Report and Points to Verify
This article is based on the user-provided news title, event timing and event summary. The event timing was described as unspecified. No specific official source link was provided in the input, so the notice and subsequent materials still need to be verified against authoritative publications.
Relevant material to monitor may include the official notice, the standards organization's draft and final documents, and any later explanations of assessment or implementation. Businesses should also watch for changes in customer specifications or tender documents, relevant trade execution and industry feedback. None of those later developments is confirmed by the information supplied for this article.
Deep Dive
Related Intelligence
 Cyber SecurityDo High-Net-Worth Buyers Prioritize Cyber Security Certifications When Sourcing Smart HVAC Controllers?Analyst:IT & Security Director
 Cyber SecurityWhat cybersecurity risks arise when integrating POS systems with building management platforms?Analyst:IT & Security Director
 Cyber SecurityHow do cyber security frameworks like NIST CSF apply to smart HVAC control networks in high-rise buildings?Analyst:IT & Security Director